Secure Healthcare Software Case Study: HIPAA, UK GDPR & UAE Health Data Controls
In This Article
- Healthcare software serving international markets cannot rely on one generic security checklist.
- The Challenge: Healthcare Security Changes Across Markets
- Secure Patient Data by Design
- Role-Based Access and Least Privilege
- Encryption and Secure Communication
- Auditability and Operational Accountability
- Secure Telemedicine Workflows
- Cloud Infrastructure and Vendor Responsibility
- Built for International Healthcare Growth
- Business Impact
- Building Secure Healthcare Software?
Healthcare software serving international markets cannot rely on one generic security checklist.
A telemedicine platform, Hospital Management System, healthcare CRM, patient portal, or mobile health application may process some of the most sensitive information an organization holds patient identities, medical histories, appointments, consultations, billing information, communications, and clinical records.
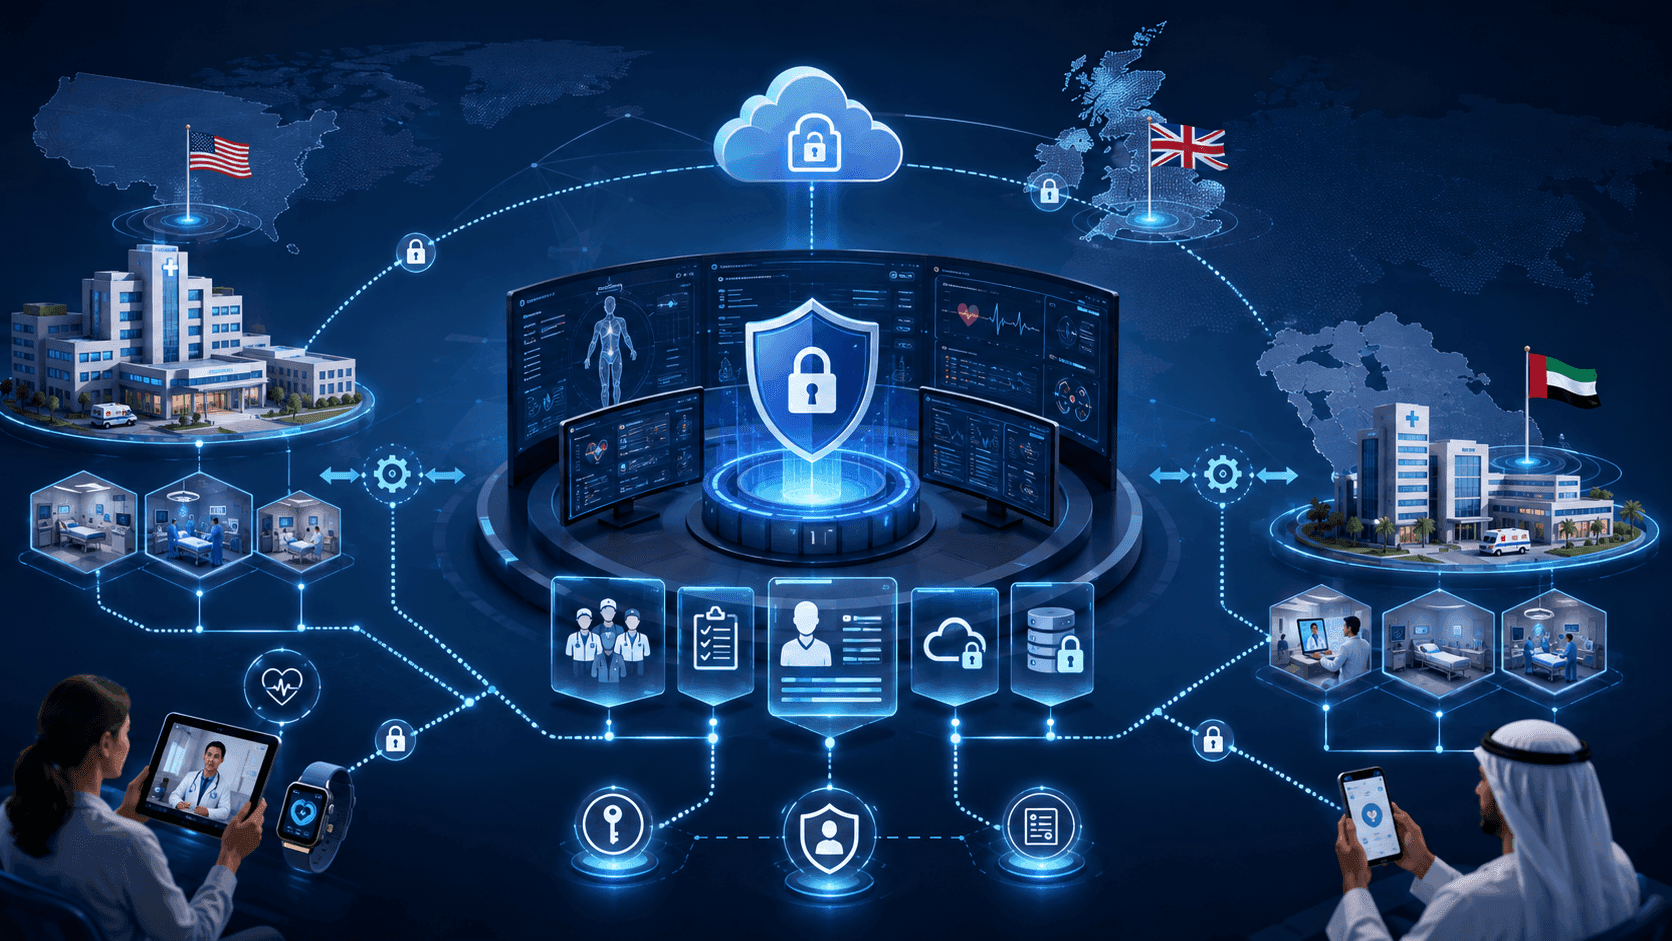
Murmu Software Infotech developed a security-focused healthcare software architecture designed for hospitals, clinics, telemedicine businesses, healthcare startups, and multi-location healthcare organizations operating across markets such as the USA, UK, and UAE. The platform combines controlled patient-data workflows, role-based access, encrypted communications, audit trails, secure telemedicine, cloud infrastructure, healthcare CRM/HMS capabilities, and workflow automation.
The objective was not simply to make healthcare software “secure.”
It was to make privacy, access control, auditability, and regional compliance considerations part of the architecture from the beginning.
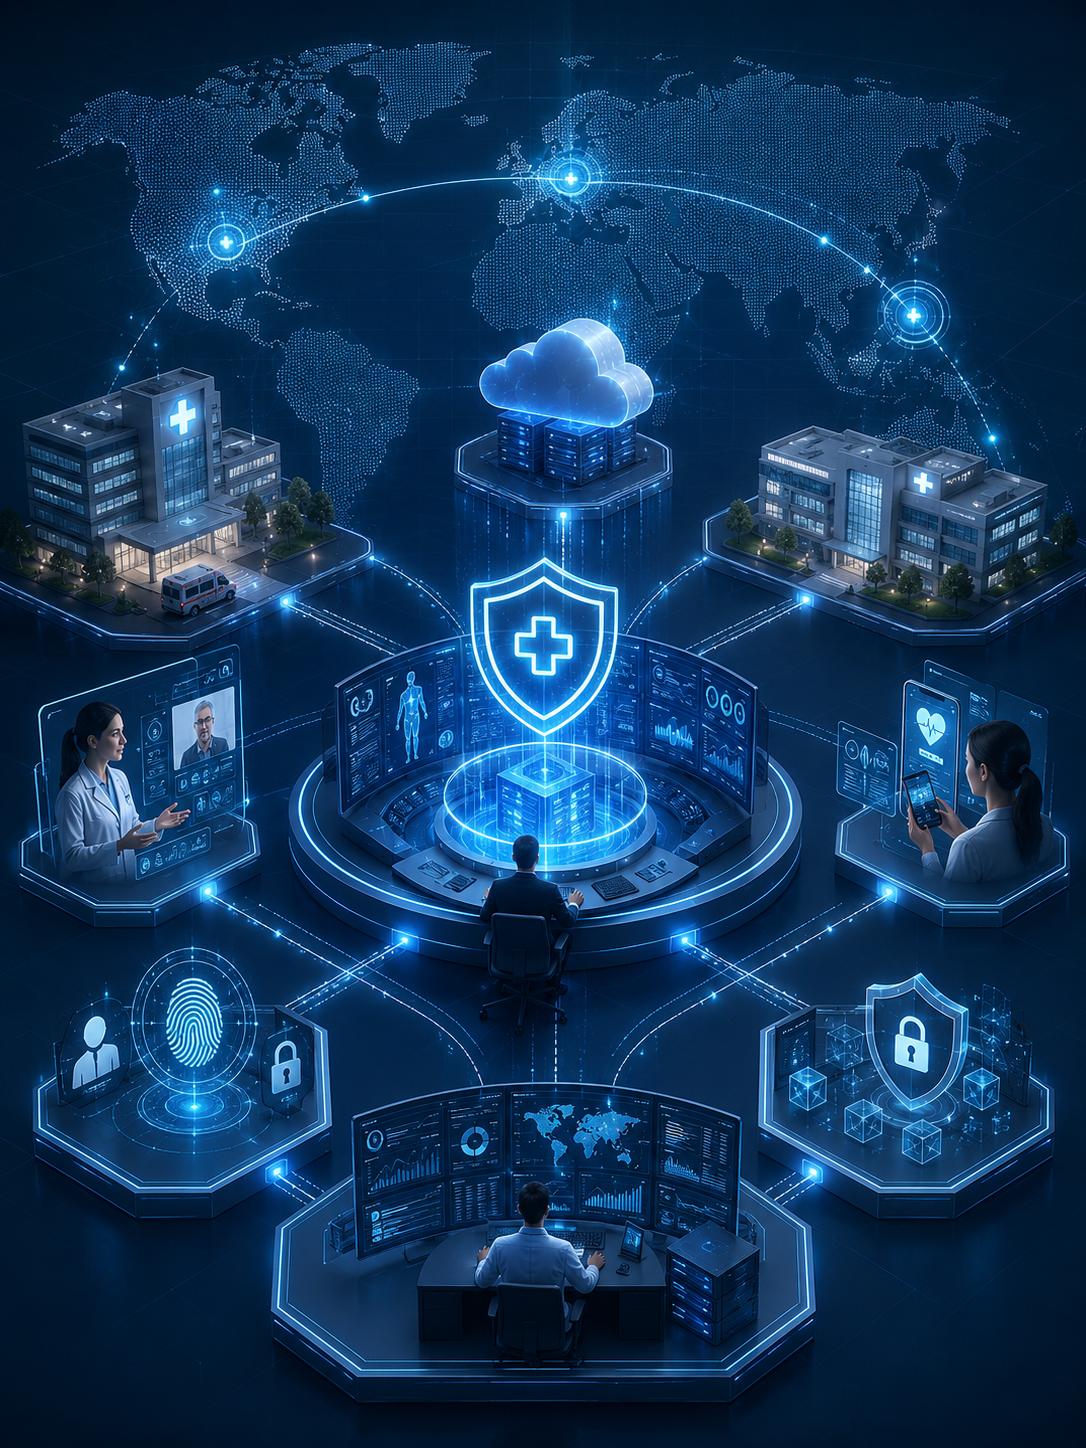
Build Secure Healthcare Across Markets
Protect patient data with secure architecture, role-based access, encrypted workflows, auditability, telemedicine security, and scalable cloud infrastructure.
The Challenge: Healthcare Security Changes Across Markets
International healthcare providers face two challenges simultaneously.
First, they must protect highly sensitive healthcare information against unauthorized access, misuse, disclosure, and operational disruption.
Second, the regulatory framework changes by geography.
In the United States, the HIPAA Security Rule requires regulated entities to protect electronic protected health information through appropriate administrative, physical, and technical safeguards, including access controls, audit controls, authentication, integrity protections, and transmission security.
In the UK, health information is treated as special-category personal data, requiring stronger protection, an appropriate lawful basis and processing condition, accountability, data minimization, security, and privacy-by-design considerations.
In the UAE, healthcare systems may need to account for the federal Personal Data Protection Law, Federal Law No. 2 of 2019 governing ICT in health fields, and applicable emirate-level health information requirements.
The platform therefore needed a security-first foundation that could be configured around market-specific obligations rather than pretending one compliance label covered every jurisdiction.
Build Secure Healthcare Software for Regulated Global Markets
Secure Patient Data by Design
The solution prioritizes protected patient-data workflows from the point information enters the system.
Patient records, digital consultations, appointment information, CRM activity, and healthcare communications are handled through controlled workflows designed to reduce unnecessary exposure.
A stronger architecture follows principles such as:
Collect only what is needed → Restrict who can access it → Protect it during storage and transmission → Record important activity → Monitor and review access.
This approach supports both healthcare security and privacy-by-design objectives.
Role-Based Access and Least Privilege
Not every healthcare employee should have access to every record.
The platform uses role-based access control to support different permissions for doctors, administrators, departments, support teams, and other authorized users.
This aligns closely with the HIPAA requirement to authorize access according to appropriate user roles and with broader international data-protection principles that emphasize limiting access to what users actually need.
The operational principle is simple:
the right person → the right information → for the right purpose.
Encryption and Secure Communication
Healthcare workflows increasingly extend beyond hospital walls.
Patients may communicate through portals, mobile applications, remote consultations, notifications, and video visits.
The solution therefore includes encrypted communication workflows and protected telemedicine infrastructure.
For U.S. HIPAA-regulated environments, transmission security is specifically part of the Security Rule.
For international deployments, encryption should form part of a broader security model that also addresses identity, access, configuration, key management, monitoring, secure APIs, and infrastructure controls.
Auditability and Operational Accountability
Healthcare organizations need to know more than whether a user can log in.
They need visibility into what users did after authentication.
The solution includes user activity logs, access monitoring, and operational audit records.
Auditability supports security investigations, governance, operational accountability, and compliance reviews.
A useful healthcare audit model records important events such as:
login → record access → update → export → administrative action → security event.
HIPAA explicitly requires mechanisms capable of recording and examining activity in systems containing or using ePHI.
Secure Telemedicine Workflows
Telemedicine introduces additional security boundaries because consultations involve patients, doctors, devices, networks, communication channels, and often third-party services.
The platform connects secure consultation workflows with healthcare access controls, patient communications, appointments, and operational systems rather than treating video calling as an isolated feature.
The resulting flow becomes:
Patient Authentication → Appointment → Authorized Doctor Access → Protected Consultation → Record Update → Audit Trail → Follow-Up
This creates a more defensible digital-care architecture.
Protect Patient Data with Compliance-Ready Healthcare Architecture
Cloud Infrastructure and Vendor Responsibility
Secure cloud deployment requires more than selecting a well-known cloud provider.
For HIPAA-regulated U.S. deployments, a cloud provider that creates, receives, maintains, or transmits ePHI on behalf of a regulated organization is generally a business associate, and appropriate Business Associate Agreements may be required.
Likewise, a software vendor that accesses PHI for hosting, troubleshooting, or related services may become a business associate.
This means compliance is a shared operational responsibility involving architecture, contracts, infrastructure configuration, policies, risk assessments, and ongoing management not a feature that developers can switch on.
Built for International Healthcare Growth
The architecture supports scalable cloud operations, multi-location healthcare workflows, healthcare CRM and HMS modules, telemedicine, automated patient communications, and international deployment patterns.
For the USA, UK, and UAE, the same core platform can therefore retain a common technology foundation while adapting privacy controls, contracts, data-location decisions, retention policies, consent requirements, access policies, and operational governance to the target jurisdiction.
Business Impact
The strongest outcome is not simply “HIPAA compliance.”
It is a more mature digital-health operating model built around:
controlled access, protected communication, auditable activity, secure cloud deployment, stronger operational visibility, scalable healthcare workflows, and privacy-conscious architecture.
That provides a stronger foundation for hospitals, telemedicine providers, and healthcare startups entering regulated international markets.
Building Secure Healthcare Software?
Murmu Software Infotech develops security-focused HMS platforms, telemedicine software, healthcare CRM, patient portals, mobile healthcare applications, cloud healthcare systems, integrations, workflow automation, and long-term healthcare software support.
The goal should not be to add compliance after development.
Secure international healthcare software starts by designing privacy, security, access control, auditability, infrastructure, and regional regulatory requirements into the platform from day one.
Frequently Asked Questions
What is HIPAA-focused healthcare software development?
HIPAA-focused healthcare software development designs applications around safeguards relevant to electronic protected health information, including controlled access, authentication, auditability, secure transmission, data integrity and appropriate operational security practices.
Does HIPAA apply to healthcare software in the UK and UAE?
Not generally. HIPAA is a United States healthcare privacy and security framework. UK healthcare data is governed by UK data-protection requirements, while UAE healthcare systems must consider applicable federal and emirate-level health-data and privacy rules.
What security controls should healthcare software include?
Common controls include role-based access, strong authentication, encrypted communications, audit logs, secure APIs, protected cloud infrastructure, monitoring, backup and recovery controls, and policies governing access to sensitive healthcare information.
What is role-based access control in healthcare software?
Role-based access control limits system functions and healthcare information according to a user's responsibilities, helping doctors, administrators, departments and support teams access only the information required for their work.
Why are audit trails important in healthcare software?
Audit trails record important activities such as authentication, access, updates and administrative actions, improving accountability, incident investigation, security monitoring and compliance review.
How can telemedicine software protect patient information?
Secure telemedicine architecture can combine authenticated access, encrypted communication, controlled patient and doctor workflows, protected data handling, audit logging and secure cloud infrastructure.
Can cloud healthcare software support HIPAA-regulated organizations?
Yes, but cloud use must be configured appropriately. When a cloud provider creates, receives, maintains or transmits ePHI for a HIPAA-regulated organization, an appropriate Business Associate Agreement and applicable safeguards may be required.
What does UK GDPR require for healthcare data?
Health information is special-category personal data under UK GDPR. Organizations generally need an Article 6 lawful basis plus an applicable Article 9 processing condition and must follow broader requirements such as security, accountability and data protection by design.
What healthcare data rules apply in the UAE?
UAE healthcare platforms may need to address federal personal-data and healthcare ICT requirements as well as local health-authority standards. Dubai healthcare entities, for example, are subject to DHA health-information governance policies and standards.
Who develops secure healthcare software for USA, UK and UAE markets?
Murmu Software Infotech develops security-focused HMS, telemedicine platforms, healthcare CRM, patient applications, cloud healthcare systems, workflow automation and international healthcare software solutions.